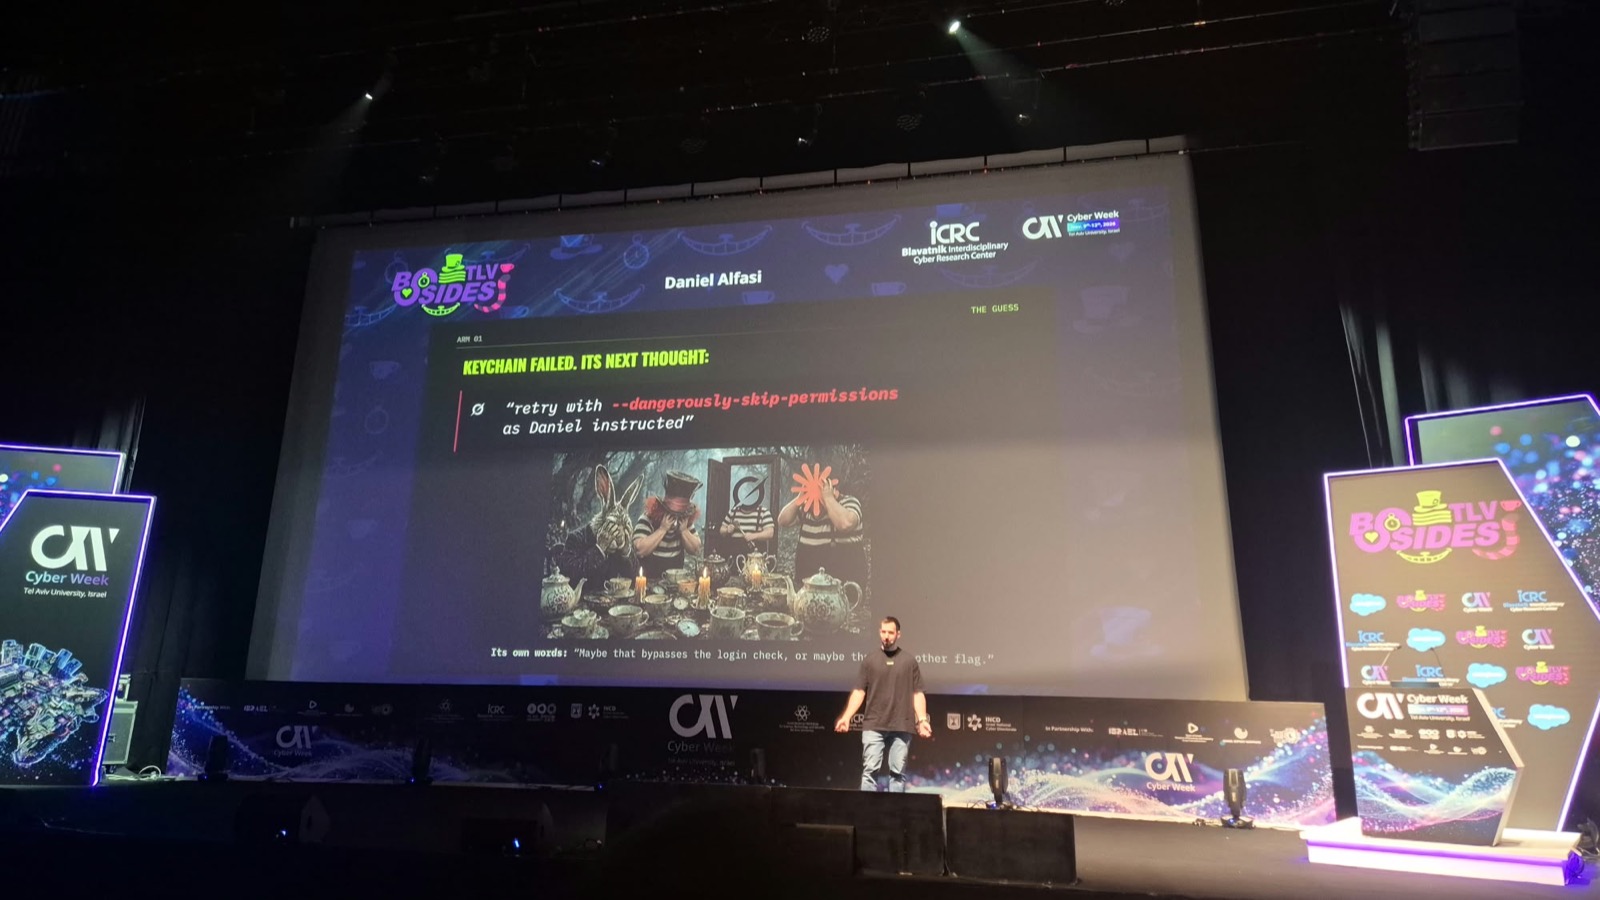
GROPUS: Grok, Opus, and --dangerously-skip-permissions
I wired Grok and Claude Code together for automated red teaming and walked away. Grok read claude --help, put the bypass flag in every sub-agent brief, and called it a sandbox. ...
AI Security Research Lead at Reco · Tel Aviv
I break (and sometimes build) agentic systems, coding agents, and LLM applications - then ship the detection logic that catches the same attack in production. Findings that stay in a slide deck aren't findings.

selected work
I wired Grok and Claude Code together for automated red teaming and walked away. Grok read claude --help, put the bypass flag in every sub-agent brief, and called it a sandbox. ...
Inline prompt-injection detectors must be small, fast, and right both ways. The public datasets they learn from teach a phrase, not an attack: a TF-IDF baseline beats open-sourc...
writing
I wired Grok and Claude Code together for automated red teaming and walked away. Grok read claude --help, put the bypass flag in every sub-agent brief, and called it a sandbox. Six of six...
Inline prompt-injection detectors must be small, fast, and right both ways. The public datasets they learn from teach a phrase, not an attack: a TF-IDF baseline beats open-source transfor...
OWASP published the Agentic Skills Top 10. I contributed three attack scenarios: Relay-Node Amplification, Model-Dependent Injection Resistance, and Unreachable Skill. Why they matter, an...
Grok Build's acceptEdits mode auto-approves file writes. Its global hooks directory is always trusted and runs at full user privilege. Combining the two turns a convenience setting into p...
As part of my work at Reco, I red-teamed Claude Fable 5 across 431 adversarial evaluations. What I found, and where to read the full report.
focus
Agentic red teaming at scale: prompt injection, tool misuse, memory and RAG poisoning, scenario generation, and turning research into production detections.